INDEPENDENT SITUATIONAL AWARENESS
CRITICALTHREAT WATCH_
THE PREPAREDNESS NEWS TERMINAL

Stay informed.
Stay one step ahead.

EST. 2026 /// SIGNAL OVER NOISE
COMMUNITY SIGNALS

Vote on stories. Share what matters.

CRITICAL THREAT WATCH

Welcome back.

Log in to vote, comment, and share stories with the community.

COMMUNITY SUBMISSION

Add a signal.

Share a link and a clear headline. Your story will be labeled as added by @.

Stories from accounts younger than seven days appear after administrator approval. Queued stories stay private until reviewed.

ON THE WIRE

Global developments. Local readiness. Original sources, ranked by readers.

RSS / ATOM / X USERS + HASHTAGS
01 /

THE LIVE WIRE

LIVE

Locations are reviewed, not inferred. Time windows apply to the live feed. Browse older entries in the archive Follow topics and manage your digest

Highest net score first: upvotes minus downvotes, then newest date.
Page 8 of 10Showing 351-400 of 466 entries
FILTERED BY
The Hacker News
SYSTEM CREATED / FEED IMPORT
TOP RANKED SIGNAL

Zyxel GS1900 Patch Fails to Block Zero-Day Exploit Allowing Root Command Execution

Zyxel GS1900 network switches that received the vendor's earlier fix for an actively exploited flaw are still open to the exploit attackers used, researchers at Binarly found. The exploit lets anyone who can reach a switch's web management interface run commands on it without logging in. Zyxel has released new firmware for 10 GS1900 models that clo

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Hackers Exploit Patched Apple Flaw to Deliver Info-Stealing Malware, CISA Says

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a medium-severity security flaw impacting multiple Apple operating systems to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability in question is CVE-2024-27834 (CVSS score: 5.5), a case of improper authentic

0
Krebs on Security
SYSTEM CREATED / FEED IMPORT

Want to Rent an Internet Address at the White House?

Several staffers at the White House are using computers or mobile devices equipped with residential proxy services that render their internet address available for others to rent, security experts warned today. One of the proxy services is a Russian company whose founder's web hosting business was ground zero for cyberattacks against election syste

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour Run

OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs. "Our prototype identified and analyzed 2,308 candidate Linux kernel findings, dynamically reproduced 1,724 vulnerabilities, an

0
The Record
SYSTEM CREATED / FEED IMPORT

More Asian airlines announce data breaches after attack on Spanish IT provider Amadeus

Japan Airlines, Cathay Pacific, Korean Air, Asiana Airlines, Singapore Airlines and Malaysia Airlines have all come forward over the last week to report data breaches traced back to Amadeus IT Group — a company that builds and maintains platforms for flight reservation, ticketing and check-in platforms.

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

The Missing Dimension of Cyber Preparedness

The technical aspect of incident response can be immense. In extreme scenarios, such as the NotPetya incident in 2017, global organisations such as the shipping company Maersk found the speed and scale of the malware’s impact to be unlike anything they’d seen before. Computer screens turned black. Employees sprinted through the offices demanding th

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Debian and Ubuntu APT Flaw Lets MitM Attackers Swap Verified Packages and Run Code as Root

A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own. The attacker's code then runs as root, according to advisories that Debian, Ubuntu, and APT's developers published on November 4. The attack needs APT to retry failed downloads, which it does by defa

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

SonicWall Won't Patch EoL GMS Flaws That Could Expose Files, Alter Database Records

SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2 and earlier versions, are below - CVE-2026-109593 (CVSS score: 9.1) - An unauthenticated file read vulnerability that could allow an attacker with

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Researchers Uncover Prompt Adware Hidden in OpenAI Codex Jailbreak Toolkit

Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research. Called Haiou (meaning Seagull in Chinese), the jai

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Sysdig Adds Runtime Security and Governance for AI Agents

Sysdig’s platform uses runtime visibility to track AI agent actions and block risky behavior before it reaches production systems. The post Sysdig Adds Runtime Security and Governance for AI Agents appeared first on SecurityWeek .

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits

The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker. "The injected JavaScript code collects browser and device attributes," Se

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Barracuda ESG Authentication Bypass Flaw Opens Path to Root

An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances. The post Barracuda ESG Authentication Bypass Flaw Opens Path to Root appeared first on SecurityWeek .

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Agentic Data Security Firm Sentra Raises $150 Million

The company will invest in agentic data security capabilities and expand its go-to-market organization. The post Agentic Data Security Firm Sentra Raises $150 Million appeared first on SecurityWeek .

0
SYSTEM CREATED / FEED IMPORT

The Classics Return: Vulnerable E-Mail Scripts, (Wed, Nov 4th)

One of the early web application vulnerabilities I remember was CVE-2000-0411 [CVE]. This was a simple vulnerability in a CGI-bin script used to send e-mail. The vulnerability was pretty straightforward: Adding additional parameters to the URL leaked environment variables. Other vulnerabilities allowed setting the "To" address and were he

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads

A critical flaw in Ruby on Rails could allow an unauthenticated attacker to write arbitrary files on an app's server by uploading a crafted file if the app processes uploads using ImageMagick. The Rails project disclosed the flaw in an advisory and fixed it in versions 8.1.4.1 and 8.0.5.2. The flaw is in Active Storage, the part of Rails that handl

0
CISA All Advisories
SYSTEM CREATED / FEED IMPORT

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2024-27834 Apple Multiple Products Improper Authentication Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Bi

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Xen Hypervisor Flaws Let One Malicious VM Read and Write Any Other VM's Memory

Two flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including dom0. Dom0 is the VM that, by default, has full permissions and manages the others. Patches are out, and there is no known mitigation, the Xen Project said in an advisory on November 3. All Xen versions

0
The Hacker News
SYSTEM CREATED / FEED IMPORT

Radio With No Radar: Why Agent Runtime Security Fails Without the Layers Beneath It

Nearly every agent security pitch now ends on the same promise: the product stops the bad action in real time. The promise holds for one kind of agent, the kind whose traffic passes through a gateway the enterprise owns. Most agents never touch one. One recent case shows what that gap looks like in practice. An employee asked an AI assistant to tri

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Malicious cPGuard Updates Served in OpsShield Supply Chain Attack

Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions. The post Malicious cPGuard Updates Served in OpsShield Supply Chain Attack appeared first on SecurityWeek .

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical

The browser update resolves dozens of memory safety bugs and incorrect/missing authorization issues. The post Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical appeared first on SecurityWeek .

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

BLUF: The Next AI Problem for Intelligence Is Not the Model, It's the Manager

The Intelligence Community has decided AI agents are coming. It has not decided how they will be supervised, checked and held to analytic standards. In April, CIA Deputy Director Michael Ellis said analysts will soon work alongside AI “coworkers” that draft key judgments and check them against tradecraft standards, and that within a decade officers

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

North Korea Launches Missiles Toward the Sea as Pyongyang Protests Against US Claims on Binance Hack

In recent months, North Korea has accelerated its weapons tests in a likely bid to increase its leverage in potential diplomacy with the US. The post North Korea Launches Missiles Toward the Sea as Pyongyang Protests Against US Claims on Binance Hack appeared first on SecurityWeek .

0
SecurityWeek
SYSTEM CREATED / FEED IMPORT

Meta Shares Top Muse Bug Bounty Findings as Payouts Reach $1.2 Million

A $300,000 award went to a pre-launch flaw that exposed conversations and tokens on internal Muse test VMs used by Meta staff. The post Meta Shares Top Muse Bug Bounty Findings as Payouts Reach $1.2 Million appeared first on SecurityWeek .

0
CISA All Advisories
SYSTEM CREATED / FEED IMPORT

Subnet Solutions PowerSYSTEM Center

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to execute unauthorized SQL commands and gain access to unauthorized resources. The following versions of Subnet Solutions PowerSYSTEM Center are affected: PowerSYSTEM Center 2020 <=5.29.x (CVE-2026-63017) PowerSYSTEM Center 2024 >=6.0.x|<=6.2.x (CVE-2026-630

0
CISA All Advisories
SYSTEM CREATED / FEED IMPORT

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-119977 WordPress Core Time-of-check Time-of-use (TOCTOU) Race Condition Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the fede

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

The Coming Age of Robotic Warfare

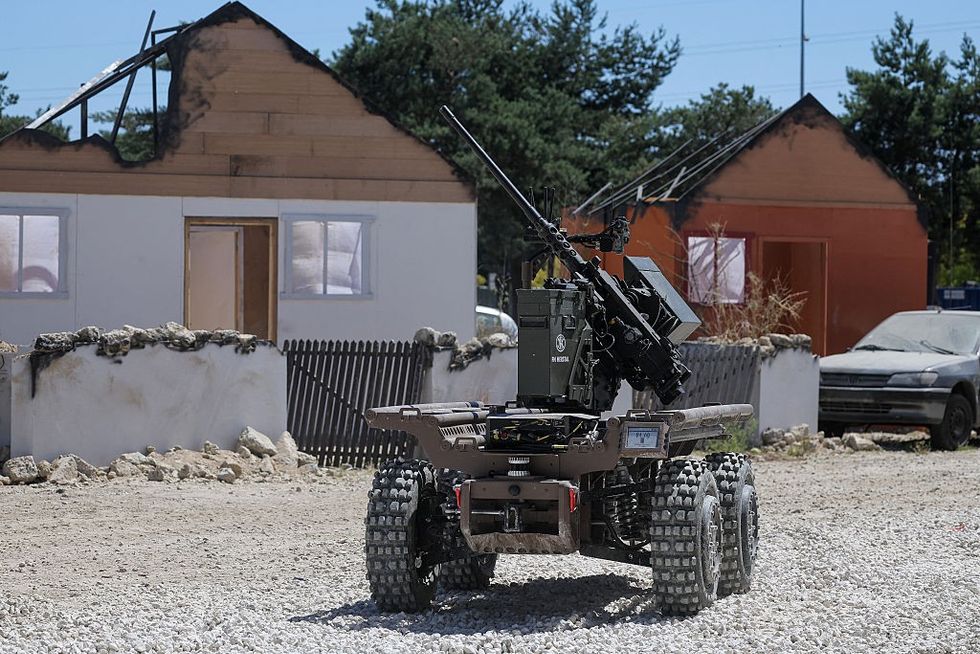
A battalion of armed robots moves against a unit of soldiers, aiming to seize territory. In the ensuing battle, the robots open fire, communicate with one another and change tactics as needed. Air cover is provided by uncrewed drones; logistical support and supplies are delivered by a separate team of robots. Territory is taken, prisoners captured.

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

The Hidden Cost of America’s War With Iran

“The [U.S. Naval Support Activity Bahrain] base and Fifth Fleet headquarters have been rendered largely inoperable for their original functions, with repairs estimated at $400 million… Chief of Naval Operations Admiral Daryl Caudle and other senior defense officials stated that the Navy will not return to full normal operations at the Bahrain facil

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

Fire Base Australia: Can America’s Southern Base Sustain a Pacific War?

American access to Australian bases is only as valuable as Australia’s ability to keep them operating under attack. For Washington, expanding military cooperation raises an operational question: can Australia sustain an American campaign while defending its own territory, infrastructure and population? For Canberra, the corresponding question is wh

0
Krebs on Security
SYSTEM CREATED / FEED IMPORT

Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies

Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user's Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the botnet's acce

0
Palo Alto Unit 42
SYSTEM CREATED / FEED IMPORT

Unit 42 Threat Intelligence Highlights - Nov. 2, 2026

Unit 42 details recent threat intelligence, highlighting cyberespionage, financial extortion, and the rapid adoption of AI across offensive workflows. The post Unit 42 Threat Intelligence Highlights - Nov. 2, 2026 appeared first on Unit 42 .

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

The Command We Must Start

In 1928, Secretary of War Dwight Davis ordered the Army to assemble an experimental mechanized force of tanks, armored cars, and motorized infantry at Camp Meade, Maryland. It was disbanded within months. A second attempt was dissolved in 1931, when the Army told each of its branches to mechanize itself. The infantry kept the tanks, the cavalry bui

0
The Cipher Brief
SYSTEM CREATED / FEED IMPORT

The Cipher Brief’s 10th Threat Conference: Optimism, Urgency, and the Imperative to Act

Which came first: The Cloister at Sea Island, the Office of Strategic Services, or the CIA? The resort wins. The Cloister first opened in 1928, fourteen years before the OSS and nineteen before CIA. It was a fitting setting for The Cipher Brief’s 10th Threat Conference, where conversations returned repeatedly to a question familiar to generations o

0
SYSTEM CREATED / FEED IMPORT

Mutipath TCP: Use and Detection, (Mon, Nov 2nd)

Last week, an often-ignored&&#x23&#x3b;x26&#x3b;&#x23&#x3b;xc2&#x3b;&&#x23&#x3b;x26&#x3b;&#x23&#x3b;xa0&#x3b;TCP option, introduced in 2020, made the news due to a new vulnerability in Linux&&#x23&#x3b;x26&#x3b;&#x23&#x3b;39&#x3b;s implementation (RFC&&#x23&#x3b;x26&#x3b;&#x23&#x3b;xc2&#x3b;&&#x23&#x3b;x26&#x3b;&#x23&#x3b;xa0&#x3b;8684, &&#x23&#x3b

0
Cloudflare Blog
SYSTEM CREATED / FEED IMPORT

How we halved DNS build delay and cut memory use by 85%

Zone setting changes used to rebuild entire DNS zones, even ones with tens of millions of records. Here is how we built a planner that picks the smallest safe build, cutting full builds by 40%, peak memory by 85%, and halving build delay.

0
ASPI Strategist
SYSTEM CREATED / FEED IMPORT

Organisations need to prove that their AI agents can shut down

Any organisation contemplating use of AI agents, especially any in national security or critical infrastructure, should give them no system access until sure that they will obey an order to stop. This is called a ...

0